Wazuh, Security Onion and Graylog are the closest fits for small security teams and MSPs that need threat detection and log analysis on a limited budget. Wazuh and Security Onion are open source platforms, and Graylog documents the same features across cloud, on-premises and air-gapped deployments. The shortlist is for lean teams that want detection coverage without building a large SOC.
The shortlist
Side-by-side comparison
| Tool | Who it is for | Platforms | Pricing |
|---|---|---|---|
 WazuhWazuh | Small teams and MSPs that want open source endpoint and SIEM coverage in one platform | Common operating systems via the agent; public cloud, private cloud and on-premises; managed Wazuh Cloud available | Pricing on wazuh.com |
 Security OnionSecurity Onion Solutions | Defenders and SOC analysts who want network and host visibility with hunting and case management | Single appliance to distributed grid; Linux desktop install option for SOC analysts | Pricing on securityonionsolutions.com |
 GraylogGraylog | Lean security, IT and audit teams that need log management with retention controls | Vendor's cloud, customer's cloud or on-premises, including air-gapped environments | Pricing on graylog.org |
 Elastic SecurityElastic | Teams that want SIEM, endpoint protection and prebuilt integrations on one platform | Cloud, self-managed and air-gapped deployments | Pricing on elastic.co |
 Microsoft SentinelMicrosoft | Teams that already use Microsoft Defender and want a cloud-native SIEM | Cloud-native; targets multi-cloud and multiplatform environments | Pricing on microsoft.com |
 Sumo Logic Cloud SIEMSumo Logic | SOC teams that want a cloud-native SIEM with detection-as-code and playbooks | Cloud-native; hosted collectors or OpenTelemetry-based installed agent | Pricing on sumologic.com |
Quick verdict by need
- Wazuh if you need small teams and MSPs that want open source endpoint and SIEM coverage in one platform.
- Security Onion if you need defenders and SOC analysts who want network and host visibility with hunting and case management.
- Graylog if you need lean security, IT and audit teams that need log management with retention controls.
- Elastic Security if you need teams that want SIEM, endpoint protection and prebuilt integrations on one platform.
- Microsoft Sentinel if you need teams that already use Microsoft Defender and want a cloud-native SIEM.
- Sumo Logic Cloud SIEM if you need sOC teams that want a cloud-native SIEM with detection-as-code and playbooks.
Tool details
#1 · Wazuh
Wazuh
Small teams and MSPs that want open source endpoint and SIEM coverage in one platform
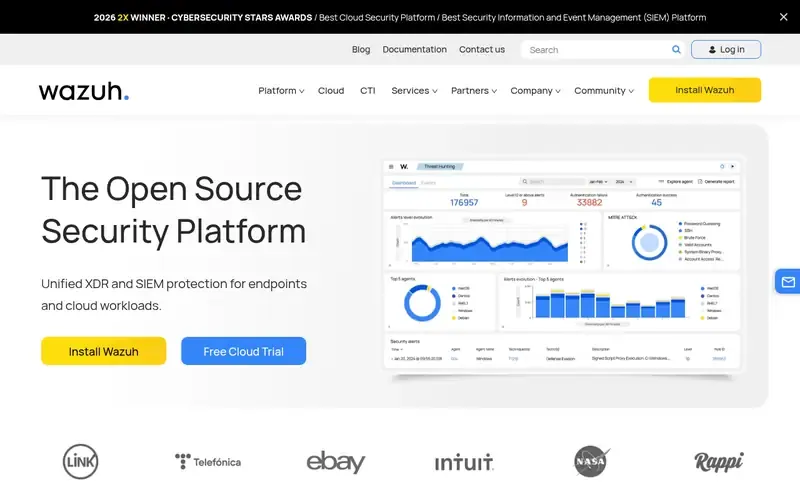
Wazuh is an open source security platform that unifies XDR and SIEM protection for endpoints and cloud workloads. It uses a single agent and platform architecture across public cloud, private cloud and on-premises data centers.
Documented strengths
- Single agent for malware detection, FIM, vulnerability assessment and configuration scanning
- Events mapped to adversary tactics and techniques
- Compliance checks against standards such as PCI-DSS, HIPAA and GDPR
- Active response with built-in or custom actions
- Integrations with VirusTotal, TheHive and PagerDuty
Documented limits
The vendor's stated audience is security analysts, so teams without analyst time should plan for how alerts will be triaged. A managed Wazuh Cloud service is offered for teams that prefer not to run the platform themselves.
- Who it is for
- Small teams and MSPs that want open source endpoint and SIEM coverage in one platform
- Platforms
- Common operating systems via the agent; public cloud, private cloud and on-premises; managed Wazuh Cloud available
- Pricing
- See the vendor's own pricing page for current plans and costs. wazuh.com
- Facts checked
- 21 November 2026
Why it is placed here: It sits first because one open source agent and platform cover detection, vulnerability assessment, compliance checks and active response, which suits a team that cannot staff several separate tools.
#2 · Security Onion Solutions
Security Onion
Defenders and SOC analysts who want network and host visibility with hunting and case management
Security Onion is an open platform for network and host visibility, intrusion detection, log management and case management. It is built for defenders and its source code is published on GitHub.
Documented strengths
- Network visibility with Suricata, Zeek, full packet capture and Strelka file analysis
- Host visibility with Elastic Agent, osquery live queries and Elastic Fleet management
- Logs flow into the Elastic stack with interfaces for alerting, hunting, dashboards and cases
- Setup wizard that builds a distributed grid quickly
- PCAP and Windows EVTX import for static analysis
Documented limits
The documentation describes a platform that scales from a single appliance to a grid of a thousand nodes, so small teams should check which deployment size fits them. The vendor offers to handle hardware and setup for teams that want to focus on threat hunting.
- Who it is for
- Defenders and SOC analysts who want network and host visibility with hunting and case management
- Platforms
- Single appliance to distributed grid; Linux desktop install option for SOC analysts
- Pricing
- See the vendor's own pricing page for current plans and costs. securityonionsolutions.com
- Facts checked
- 21 November 2026
Why it is placed here: It sits second because it bundles network capture, host visibility and case management in one install with a Setup wizard, giving strong detection coverage where a team wants to hunt on network data.
#3 · Graylog
Graylog
Lean security, IT and audit teams that need log management with retention controls
Graylog is a centralized log management and SIEM platform for capturing, storing and analyzing machine data in real time. It began in 2009 as an open source log management project and grew into a full SIEM on the same codebase.
Documented strengths
- Logs from varied sources on one timeline with consistent field names
- Built-in data lake and policy-driven tiering and retention
- Pre-built detection content for common sources, attack frameworks and audit standards
- Tuning Advisor that finds noisy alerts and recommends changes
- Machine learning baselines for users, hosts and applications
Documented limits
Data routing and tiering is listed as available in the Graylog Open edition as well as Security and Enterprise, but teams should check the vendor documentation for which other features belong to which edition. AI agents only recommend actions, and analysts approve changes.
- Who it is for
- Lean security, IT and audit teams that need log management with retention controls
- Platforms
- Vendor's cloud, customer's cloud or on-premises, including air-gapped environments
- Pricing
- See the vendor's own pricing page for current plans and costs. graylog.org
- Facts checked
- 21 November 2026
Why it is placed here: It sits third because it is aimed at lean security, IT and audit teams and documents the same features across cloud, on-premises and air-gapped deployments.
#4 · Elastic
Elastic Security
Teams that want SIEM, endpoint protection and prebuilt integrations on one platform
Elastic Security is an open, agentic security operations platform that combines SIEM, endpoint security and automation. It uses a unified data model and a single query language.
Documented strengths
- 400+ prebuilt integrations that normalize data and ship with dashboards
- Detection rules written by Elastic's research team and published openly on GitHub
- Attack Discovery that correlates scattered alerts into attack chains
- Archived data stays queryable in place without rehydration
- Automatic Migration for moving detection rules and dashboards from another SIEM
Documented limits
The platform is documented as broad, spanning SIEM, XDR, endpoint protection and an agentic layer, so small teams should decide which parts they will use. Consequential actions in the agentic layer stay human-gated, which means analyst time is still needed.
- Who it is for
- Teams that want SIEM, endpoint protection and prebuilt integrations on one platform
- Platforms
- Cloud, self-managed and air-gapped deployments
- Pricing
- See the vendor's own pricing page for current plans and costs. elastic.co
- Facts checked
- 21 November 2026
Why it is placed here: It sits fourth because its documented depth, including endpoint protection, openly published detection rules and many integrations, suits teams with some capacity to configure a larger platform.
#5 · Microsoft
Microsoft Sentinel
Teams that already use Microsoft Defender and want a cloud-native SIEM
Microsoft Sentinel is a cloud-native SIEM with a built-in data lake that also provides SOAR, UEBA, threat intelligence and AI-assisted workflows. It is unified in the Microsoft Defender experience.
Documented strengths
- Ingestion from 400+ connectors plus a no-code framework for custom connectors
- Built-in data lake for long-term log retention and hunting
- Built-in SOAR with out-of-the-box playbooks and codeless automation
- Built-in UEBA that baselines normal activity
- Security Copilot to summarize incidents and draft KQL queries
Documented limits
Documented as cloud-native and aimed at security leaders, SOC teams and analysts, so teams that need an on-premises deployment should check the vendor documentation. Teams not using Microsoft Defender should confirm how the unified experience applies to them.
- Who it is for
- Teams that already use Microsoft Defender and want a cloud-native SIEM
- Platforms
- Cloud-native; targets multi-cloud and multiplatform environments
- Pricing
- See the vendor's own pricing page for current plans and costs. microsoft.com
- Facts checked
- 21 November 2026
Why it is placed here: It sits fifth because its documented strengths are strongest for teams already working in Microsoft Defender, and it is cloud-native only, which gives small teams fewer deployment choices.
#6 · Sumo Logic
Sumo Logic Cloud SIEM
SOC teams that want a cloud-native SIEM with detection-as-code and playbooks
Sumo Logic SIEM is a cloud-native SIEM that gives SOC teams real-time threat detection, automated investigation and response automation. It is part of a broader cloud-native security platform powered by logs.
Documented strengths
- SOC Analyst Agent that gives an evidence-backed verdict with rationale
- MITRE ATT&CK Coverage Explorer showing which tactics and techniques SIEM rules cover
- Detection-as-Code support for versioning SIEM rules in GitHub
- Out-of-the-box integrations and playbooks, plus custom playbooks
- Collection through hosted collectors or an OpenTelemetry-based installed agent
Documented limits
Documented as a cloud-native platform, so teams that require self-hosting should check the vendor documentation. A FedRAMP Moderate environment is listed for the US public sector.
- Who it is for
- SOC teams that want a cloud-native SIEM with detection-as-code and playbooks
- Platforms
- Cloud-native; hosted collectors or OpenTelemetry-based installed agent
- Pricing
- See the vendor's own pricing page for current plans and costs. sumologic.com
- Facts checked
- 21 November 2026
Why it is placed here: It sits last because it is documented as a cloud-native platform for SOC teams, so it is the least aimed at lean teams that want open source or flexible self-managed deployment.
Sources
- Wazuh: wazuh.com, wazuh.com/about-us, wazuh.com/platform/xdr (21 Nov 2026)
- Security Onion: securityonionsolutions.com/software (21 Nov 2026)
- Graylog: graylog.org, graylog.org/feature, graylog.org/feature/ai (21 Nov 2026)
- Elastic Security: elastic.co/security, elastic.co/about, elastic.co/about (21 Nov 2026)
- Microsoft Sentinel: microsoft.com/en/security/business/siem-and-xdr/microsoft-sentinel-siem (21 Nov 2026)
- Sumo Logic Cloud SIEM: sumologic.com/solutions/siem, sumologic.com/platform, sumologic.com/de/solutions/siem (21 Nov 2026)
Related guides
How we compiled this
We looked at three things: fit with threat detection and log analysis for small teams, documented capabilities such as detection content, endpoint and network coverage, retention and automation, and the deployment documentation each vendor publishes. Open source availability and straightforward deployment carry weight because the audience has limited staff and budget.
All facts come from official vendor pages, each with a check date on record. The order reflects editorial fit for small teams and MSPs, combining ease of deployment, documented detection coverage and suitability for lean operations, and each position is explained in words. The list is built from documentation, not from product trials, and this page makes no cost claims, so teams should confirm commercial terms with each vendor.
Order used: Ordered by value for small teams, combining low cost, ease of deployment and detection coverage, closest fit first.
Common questions
What is the difference between a SIEM and log management?
Log management captures, stores and analyzes machine data, while a SIEM adds detection, correlation and alerting on top. Graylog documents both, having grown from open source log management into a full SIEM on the same codebase.
Which of these SIEM tools are open source?
Wazuh and Security Onion describe themselves as open platforms, and Graylog offers a Graylog Open edition. Elastic publishes its detection rules openly on GitHub. Microsoft Sentinel and Sumo Logic SIEM are described as cloud-native platforms.
Can a small team run a SIEM without a large SOC?
Wazuh uses a single agent and platform for XDR and SIEM, and Security Onion's Setup wizard builds a distributed grid quickly. Graylog is aimed at lean security, IT and audit teams. Teams should still plan for who triages alerts.
Which tools support compliance checks and long-term retention?
Wazuh runs compliance checks against standards such as PCI-DSS, HIPAA and GDPR. Graylog offers tiering and policy-driven retention to support audits, and Microsoft Sentinel provides a built-in data lake for long-term log retention.
Which options can be deployed on-premises or air-gapped?
Graylog documents cloud, customer-cloud and on-premises deployment, including air-gapped environments, with the same features everywhere. Elastic Security offers model choice across cloud, self-managed and air-gapped deployments, and Wazuh covers on-premises data centers.
The editorial order is unpaid. A vendor can buy one labelled featured slot per guide, but it gets the same fact check as everyone else and cannot alter or remove a competitor's entry. Guidehurst is independent. Product names and logos belong to their respective owners.