Shibboleth, Keycloak and Gluu Server are the first three tools on this shortlist for federated single sign-on across campuses, partner institutions and research services. It is written for university IT and research computing teams, and it starts with software built around academic federation before moving to general enterprise identity providers such as Microsoft Entra ID, Ping Identity PingOne and Okta Workforce Identity.
The shortlist
Side-by-side comparison
| Tool | Who it is for | Platforms | Pricing |
|---|---|---|---|
 ShibbolethShibboleth Consortium | Academic institutions and identity federations with complex identity needs | Service Provider supports multiple platforms, including Windows and OSX | Pricing on shibboleth.net |
 KeycloakKeycloak Project (CNCF) | Teams that want an open source identity broker in front of campus directories | A server container image is documented; other platforms are not stated on official pages | Pricing on keycloak.org |
 Gluu ServerGluu | Enterprise-style IAM with self-hosting and policy-based authorization | Self-hosted or Gluu-operated; operating systems not stated on official pages | Pricing on gluu.org |
 Microsoft Entra IDMicrosoft | Institutions managing workforce access across cloud and on-premises apps | Cloud service covering cloud and on-premises applications | Pricing on microsoft.com |
 Ping Identity PingOnePing Identity | Mixed workforce and partner access with flexible deployment | Cloud, on-premises and hybrid deployment | Pricing on pingidentity.com |
 Okta Workforce IdentityOkta | Central SSO across a large catalog of SaaS and legacy applications | Cloud platform with on-premises app access through Okta Access Gateway | Pricing on okta.com |
Quick verdict by need
- Shibboleth if you need academic institutions and identity federations with complex identity needs.
- Keycloak if you need teams that want an open source identity broker in front of campus directories.
- Gluu Server if you need enterprise-style IAM with self-hosting and policy-based authorization.
- Microsoft Entra ID if you need institutions managing workforce access across cloud and on-premises apps.
- Ping Identity PingOne if you need mixed workforce and partner access with flexible deployment.
- Okta Workforce Identity if you need central SSO across a large catalog of SaaS and legacy applications.
Tool details
#1 · Shibboleth Consortium
Shibboleth
Academic institutions and identity federations with complex identity needs
shibboleth.netShibboleth is open-source identity management software from the Shibboleth Consortium. It includes a Single Sign-On Identity Provider and a Service Provider.
Documented strengths
- Identity Provider for single sign-on with built-in support for a range of authentication systems
- Service Provider that integrates with popular web servers and offers authorisation features
- Embedded Discovery Service listing Identity Providers, with screen reader support
- Metadata Aggregator with a web service for querying processed metadata
- Community-driven development roadmap
Documented limits
The vendor describes software for organisations with complex identity management requirements, so teams should check the documentation for the operational effort that involves. The facts do not list a hosted option.
- Who it is for
- Academic institutions and identity federations with complex identity needs
- Platforms
- Service Provider supports multiple platforms, including Windows and OSX
- Pricing
- See the vendor's own pricing page for current plans and costs. shibboleth.net
- Facts checked
- 22 November 2026
Why it is placed here: It comes first because the vendor names academic institutions and identity federations as adopters, and it ships federation-specific components such as a discovery service and a metadata aggregator.
#2 · Keycloak Project (CNCF)
Keycloak
Teams that want an open source identity broker in front of campus directories
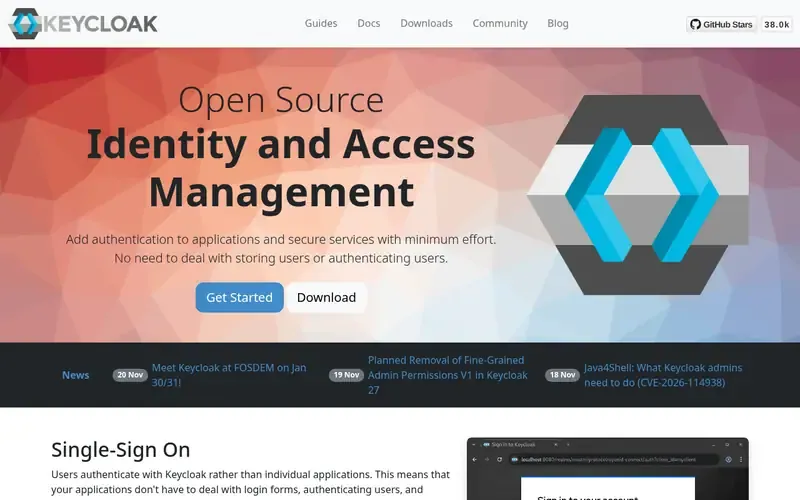
Keycloak is open source identity and access management software that adds single sign-on and authentication to applications and services. It is a Cloud Native Computing Foundation project.
Documented strengths
- Single sign-on and single sign-out across applications
- Brokering to existing OpenID Connect or SAML 2.0 identity providers
- Built-in LDAP and Active Directory connectivity
- Admin console and user account console, plus a documented administration REST API
- Clustering, customizable themes and fine-grained authorization services
Documented limits
The vendor frames Keycloak for application developers and administrators securing applications and services. Teams that need academic federation features such as metadata aggregation should check the vendor documentation.
- Who it is for
- Teams that want an open source identity broker in front of campus directories
- Platforms
- A server container image is documented; other platforms are not stated on official pages
- Pricing
- See the vendor's own pricing page for current plans and costs. keycloak.org
- Facts checked
- 21 November 2026
Why it is placed here: It sits second because it brokers authentication to existing SAML 2.0 and OpenID Connect identity providers and connects to LDAP and Active Directory, which suits partner and campus directories.
#3 · Gluu
Gluu Server
Enterprise-style IAM with self-hosting and policy-based authorization
Gluu provides enterprise identity and access management built on open source. It began as Gluu Server and is now centred on Gluu Flex and the Cedarling.
Documented strengths
- Self-hosting, or Gluu operating the infrastructure
- Cedarling, an open source embeddable policy decision point written in Rust
- Flex authentication of both people and software through configurable flows
- Self-service portal for managing MFA credentials, including FIDO passkeys
- Code and releases published on GitHub
Documented limits
The facts focus on authorization, policy and tokens, and do not describe academic federation metadata or discovery. Teams that need those should check the vendor documentation.
- Who it is for
- Enterprise-style IAM with self-hosting and policy-based authorization
- Platforms
- Self-hosted or Gluu-operated; operating systems not stated on official pages
- Pricing
- See the vendor's own pricing page for current plans and costs. gluu.org
- Facts checked
- 22 November 2026
Why it is placed here: It follows Keycloak because it is open-source-based and can be self-hosted, but its current documentation emphasises authorization and policy more than academic federation.
#4 · Microsoft
Microsoft Entra ID
Institutions managing workforce access across cloud and on-premises apps
Microsoft Entra ID is Microsoft's cloud identity and access management solution, formerly known as Azure AD. It supports SSO, MFA, passwordless sign-in and Zero Trust.
Documented strengths
- SSO connecting the workforce to apps from any location and device
- MFA, passwordless authentication and self-service portals
- Conditional access with adaptive policies
- Privileged identity management with just-in-time, least-privilege access
- Microsoft states a 99.99% monthly service resiliency guarantee
Documented limits
The vendor documents Entra ID for workforce and employee sign-in. Teams that need federation with partner institutions' identity providers should check the vendor documentation.
- Who it is for
- Institutions managing workforce access across cloud and on-premises apps
- Platforms
- Cloud service covering cloud and on-premises applications
- Pricing
- See the vendor's own pricing page for current plans and costs. microsoft.com
- Facts checked
- 21 November 2026
Why it is placed here: It is the first general enterprise provider on the list, a natural fit where campus staff already work in Microsoft environments and need one control point across cloud and on-premises applications.
#5 · Ping Identity
Ping Identity PingOne
Mixed workforce and partner access with flexible deployment
Ping Identity offers a cloud identity and access management platform covering SSO, MFA, governance, orchestration and fraud protection for workforce, partner and customer identities.
Documented strengths
- Cloud, on-premises and hybrid deployment
- Single sign-on and adaptive authentication
- No-code drag-and-drop interface for identity workflows
- Automated onboarding and offboarding, and governance features
- Services selectable individually without vendor lock-in
Documented limits
The facts describe workforce, contractor and partner access in general terms and do not mention academic federation standards. Teams that need them should check the vendor documentation.
- Who it is for
- Mixed workforce and partner access with flexible deployment
- Platforms
- Cloud, on-premises and hybrid deployment
- Pricing
- See the vendor's own pricing page for current plans and costs. pingidentity.com
- Facts checked
- 21 November 2026
Why it is placed here: It follows Entra ID because its documented partner and contractor access, plus cloud, on-premises and hybrid deployment, suit multi-institution arrangements.
#6 · Okta
Okta Workforce Identity
Central SSO across a large catalog of SaaS and legacy applications
Okta Workforce Identity Single Sign-On gives employees, contractors, partners and AI agents secure access to applications through a unified identity platform.
Documented strengths
- Cloud federation with phishing-resistant MFA
- Pre-built integrations that need no custom code
- SaaS and legacy on-premises apps via Okta Integration Network and Okta Access Gateway
- Unification of directories such as AD, LDAP and HR
- Deactivating a user revokes access to all integrated SSO applications
Documented limits
The documentation is aimed at workforce access for employees, contractors and business partners. Teams that need research-service federation between institutions should check the vendor documentation.
- Who it is for
- Central SSO across a large catalog of SaaS and legacy applications
- Platforms
- Cloud platform with on-premises app access through Okta Access Gateway
- Pricing
- See the vendor's own pricing page for current plans and costs. okta.com
- Facts checked
- 21 November 2026
Why it is placed here: It closes the list because it centres on workforce single sign-on and an application catalog, with cloud federation documented only in general terms.
Sources
- Shibboleth: shibboleth.net, shibboleth.net/about-us, shibboleth.net/products (22 Nov 2026)
- Keycloak: keycloak.org, keycloak.org/documentation (21 Nov 2026)
- Gluu Server: gluu.org, gluu.org/about (22 Nov 2026)
- Microsoft Entra ID: microsoft.com/en/security/business/identity-access/microsoft-entra-id (21 Nov 2026)
- Ping Identity PingOne: pingidentity.com/en.html, pingidentity.com/en/platform.html, pingidentity.com/en/solution.html (21 Nov 2026)
- Okta Workforce Identity: okta.com/products/single-sign-on-workforce-identity, okta.com/solutions, okta.com/solutions/secure-ai (21 Nov 2026)
Related guides
How we compiled this
We looked at how well each tool fits federated sign-on between institutions: documented single sign-on, support for federation standards such as SAML and OpenID Connect, directory connectivity, and deployment and platform documentation. The order reflects editorial fit for this use case. Tools whose documentation centres on academic federation come first, and general enterprise identity providers follow. That is a statement about fit for this scenario, not about overall quality.
Every fact comes from the vendor's official pages, and each page is recorded with the date we checked it. The list is built from documentation, not product trials, so we describe what vendors state and not how the software behaves in your environment. Pricing is not covered here. Please check each vendor's own pricing page and confirm that a tool's documented scope matches your federation requirements.
Order used: Ordered by fit with academic federation standards first, then general enterprise identity providers.
Common questions
What is identity federation for universities?
It lets people from one institution sign in to services run by another with their home credentials. Shibboleth is described by its vendor as software for identity federations, with an Identity Provider, a Service Provider and a discovery service.
Which tools on this list are open source?
Shibboleth and Keycloak are described as open source. Gluu is described as enterprise IAM built on open source, and its code and releases are published on GitHub.
Can these tools connect to existing campus directories?
Keycloak documents built-in LDAP and Active Directory connectivity, and Okta can unify directories such as AD, LDAP and HR. Entra ID centralizes identities across cloud and on-premises applications.
Do these tools support SAML and OpenID Connect?
Keycloak is based on OpenID Connect, OAuth 2.0 and SAML, and can broker to existing OpenID Connect or SAML 2.0 identity providers. For the other tools, check the vendor documentation for the protocols you need.
Which options support hybrid deployment?
Ping Identity documents cloud, on-premises and hybrid deployment. Gluu can be self-hosted or operated by Gluu, and Keycloak has a documented server container image.
The editorial order is unpaid. A vendor can buy one labelled featured slot per guide, but it gets the same fact check as everyone else and cannot alter or remove a competitor's entry. Guidehurst is independent. Product names and logos belong to their respective owners.